Keep each tool in its own lane
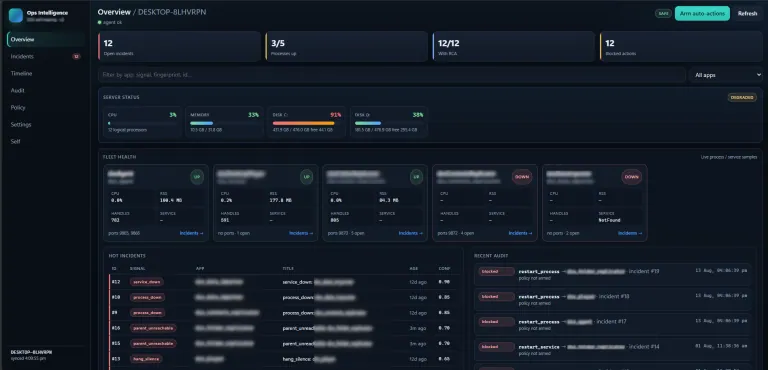
Every source connects through an isolated agent. One integration failing, or one noisy feed, cannot take the board down or starve the others.
25tools, one normalised store
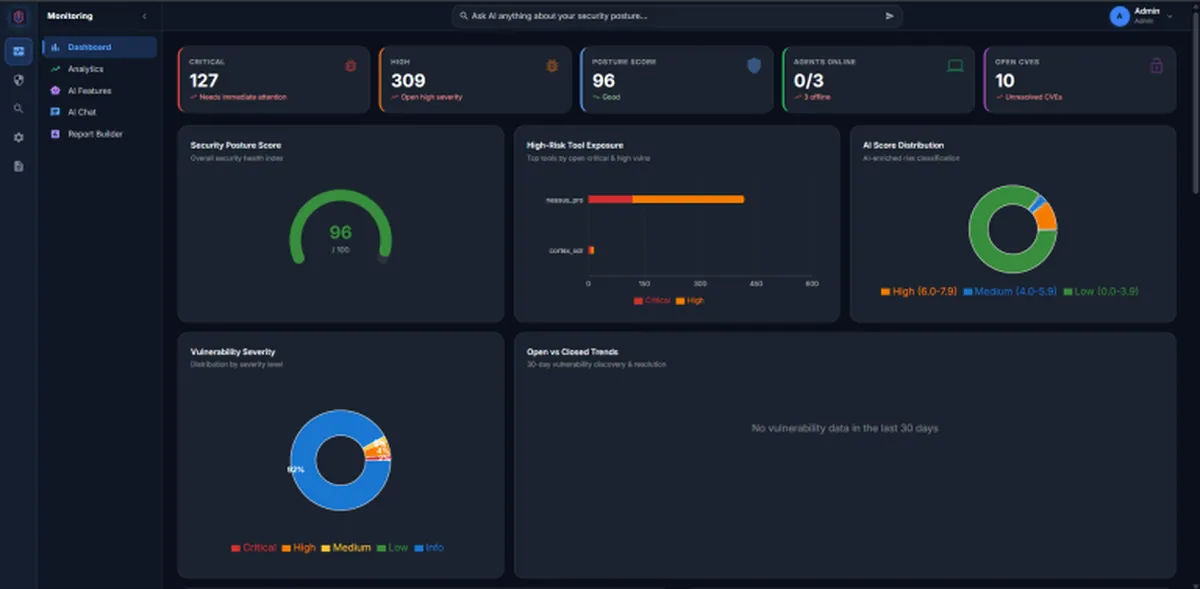
SecBoard is a vulnerability command centre. The team using it was already running about twenty-five tools across eight categories, each with its own vocabulary and its own idea of what severe means.
The backlog that came out of that was not a ranking. Everything arrived marked urgent, so nothing was. A question about the real risk meant opening several dashboards and assembling the story by hand.
Every source connects through an isolated agent. One integration failing, or one noisy feed, cannot take the board down or starve the others.
25tools, one normalised store
CVSS is an input. The risk engine also weighs reachability, how critical the asset is, and whether the exploit is actually in use.
Judgedreach, asset and exploit together
A question about exposure resolves against the normalised store, not a cached summary. That is what makes the board readable outside the security team.
Ask itplain language, on the live store
The build
The development problem was normalisation. Twenty-five feeds and no shared scale. Drop a signal while merging them and the board is a nicer view of a worse decision. Keep every signal and someone still has to decide which ones matter today.
Each tool has its own agent. That is more work up front. It is also why a vendor changing an API does not blank the board, and why a chatty scanner cannot crowd out a quieter source that happens to be right. The correlation graph those agents feed is the one store both the risk engine and the questions read.
A high score on an asset nothing can reach is a different problem from a moderate score on something an attacker would hit first. The engine holds reachability, asset criticality and exploit activity together, so the queue is what someone should open next.
The language layer sits on that same store. Someone outside the security team can ask what the exposure is and get an answer from the data. Compliance evidence comes off the same graph, so an audit is an export rather than a reconstruction done the week before the auditor arrives.
How we worked
Every tool is convinced its severity scale is the real one. The work is to keep the facts and let go of the ranking.
A board that shares its fate with any one integration is not resilient in any way that matters on a Monday morning.
A plain-language answer is only useful if it hits the store. A paragraph written last week is a different product.
Technology
More work
Tell us what you are trying to ship and an engineer will reply within one business day.